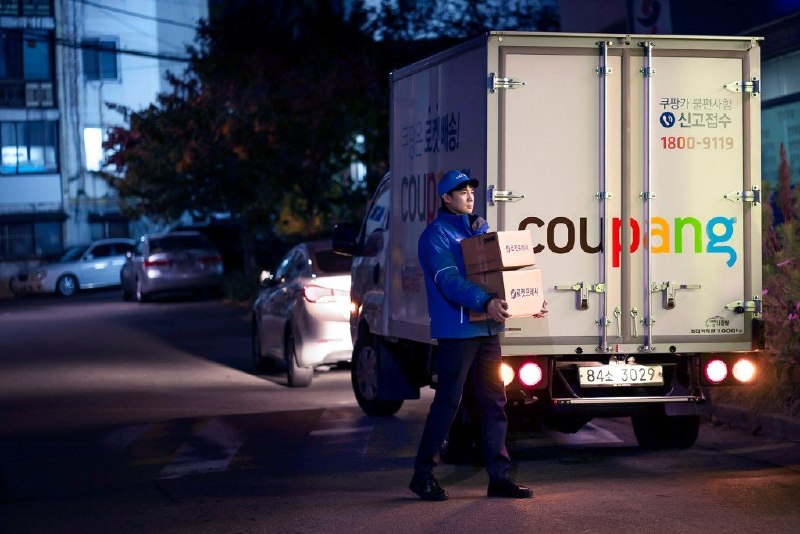
South Korea has fined online retailer Coupang a record $409 million for the country after the largest personal data breach in its history. The incident affected more than 33 million users — nearly two-thirds of the country's population. According to the regulator, the cause was inadequate internal security measures that allowed a former employee of the company to access customer information for several months.
This case continues a global trend toward tougher accountability for protecting personal data. A key starting point was the European Union's GDPR, which came into force in 2018 and made it possible to impose fines of up to 4% of a company's global turnover. After that, high-profile cases involving British Airways and Marriott cemented the principle that businesses are responsible for failing to adequately protect information.
In the United States, the largest example was Equifax's settlement of up to $700 million after a breach of data belonging to 147 million people. Another precedent was the Uber case, in which the company was penalized not only for the breach of information on 57 million users, but also for trying to conceal the fact of the hack. Later, regulators also began actively fining companies for unlawful processing of personal data, which led to record sanctions against Amazon and Meta.
Today, personal data is increasingly seen as a full-fledged economic asset. A name, phone number, purchase history, medical information and location data require the same level of protection as financial information. That is why investments in cybersecurity are becoming not an additional expense for companies, but a mandatory element of modern business.